What Is Insecure Design and How Do You Prevent It?
Your application passes every automated test and still ships a flaw an attacker walks right through. The weakness lives in the design, not the code. OWASP ranks insecure design the fourth most serious web application security risk, mapping it to 40 separate weakness types and more than 262,000 recorded occurrences. You will not patch your way out of it. A security control the blueprint never included is a control no developer will ever write.
Insecure design describes missing or ineffective security controls at the architecture stage. The weakness enters the product before anyone writes a line of code. Statistics Canada reported in October 2026 a national incident rate of 16 percent, meaning one in six Canadian businesses took a cyber security incident during 2025. Among the firms hit, attackers exploited software, hardware, or network weaknesses in 23 percent of cases. Many of those openings trace back to a decision made in a design meeting, not a coding slip.
Insecure design is not insecure implementation
A secure design still ships with implementation defects. A developer fumbles input handling, mishandles a session, or leaves a debug route open. You fix those faults with better code and better testing. Insecure design works differently. The security control the system needed was never specified, so clean code restores nothing. OWASP draws the line clearly. Design flaws and coding defects have separate root causes and separate fixes. Treating one as the other wastes your effort and leaves the real hole open.
What insecure design looks like in practice
OWASP offers three scenarios worth study. The first is a credential recovery flow built on security questions. Several people often know your mother’s maiden name or your first school, so the answers prove little. NIST 800-63b and the OWASP Application Security Verification Standard both reject the pattern. The second is a cinema chain offering a group discount for up to fifteen seats before a deposit applies. An attacker books hundreds of seats across every location in a handful of requests and drains revenue. The third is an online store with no anti-automation design. Scalper bots sweep every high-demand product within seconds of release. Each failure is business logic working exactly as written. The design never accounted for abuse.
Build security into the first blueprint
The Canadian Centre for Cyber Security and its international partners published joint guidance on a software security code of practice, built around secure-by-design principles. The message is direct. Security belongs in your earliest design decisions, not bolted on near launch. ITSG-33, the Government of Canada control framework for federal systems, takes the same lifecycle view. You select and build the controls as part of the system from the start, then carry them through operation and retirement. For smaller organizations, the CCCS Baseline Cyber Security Controls give a practical starting set without a heavy program.
Threat modeling is the core skill
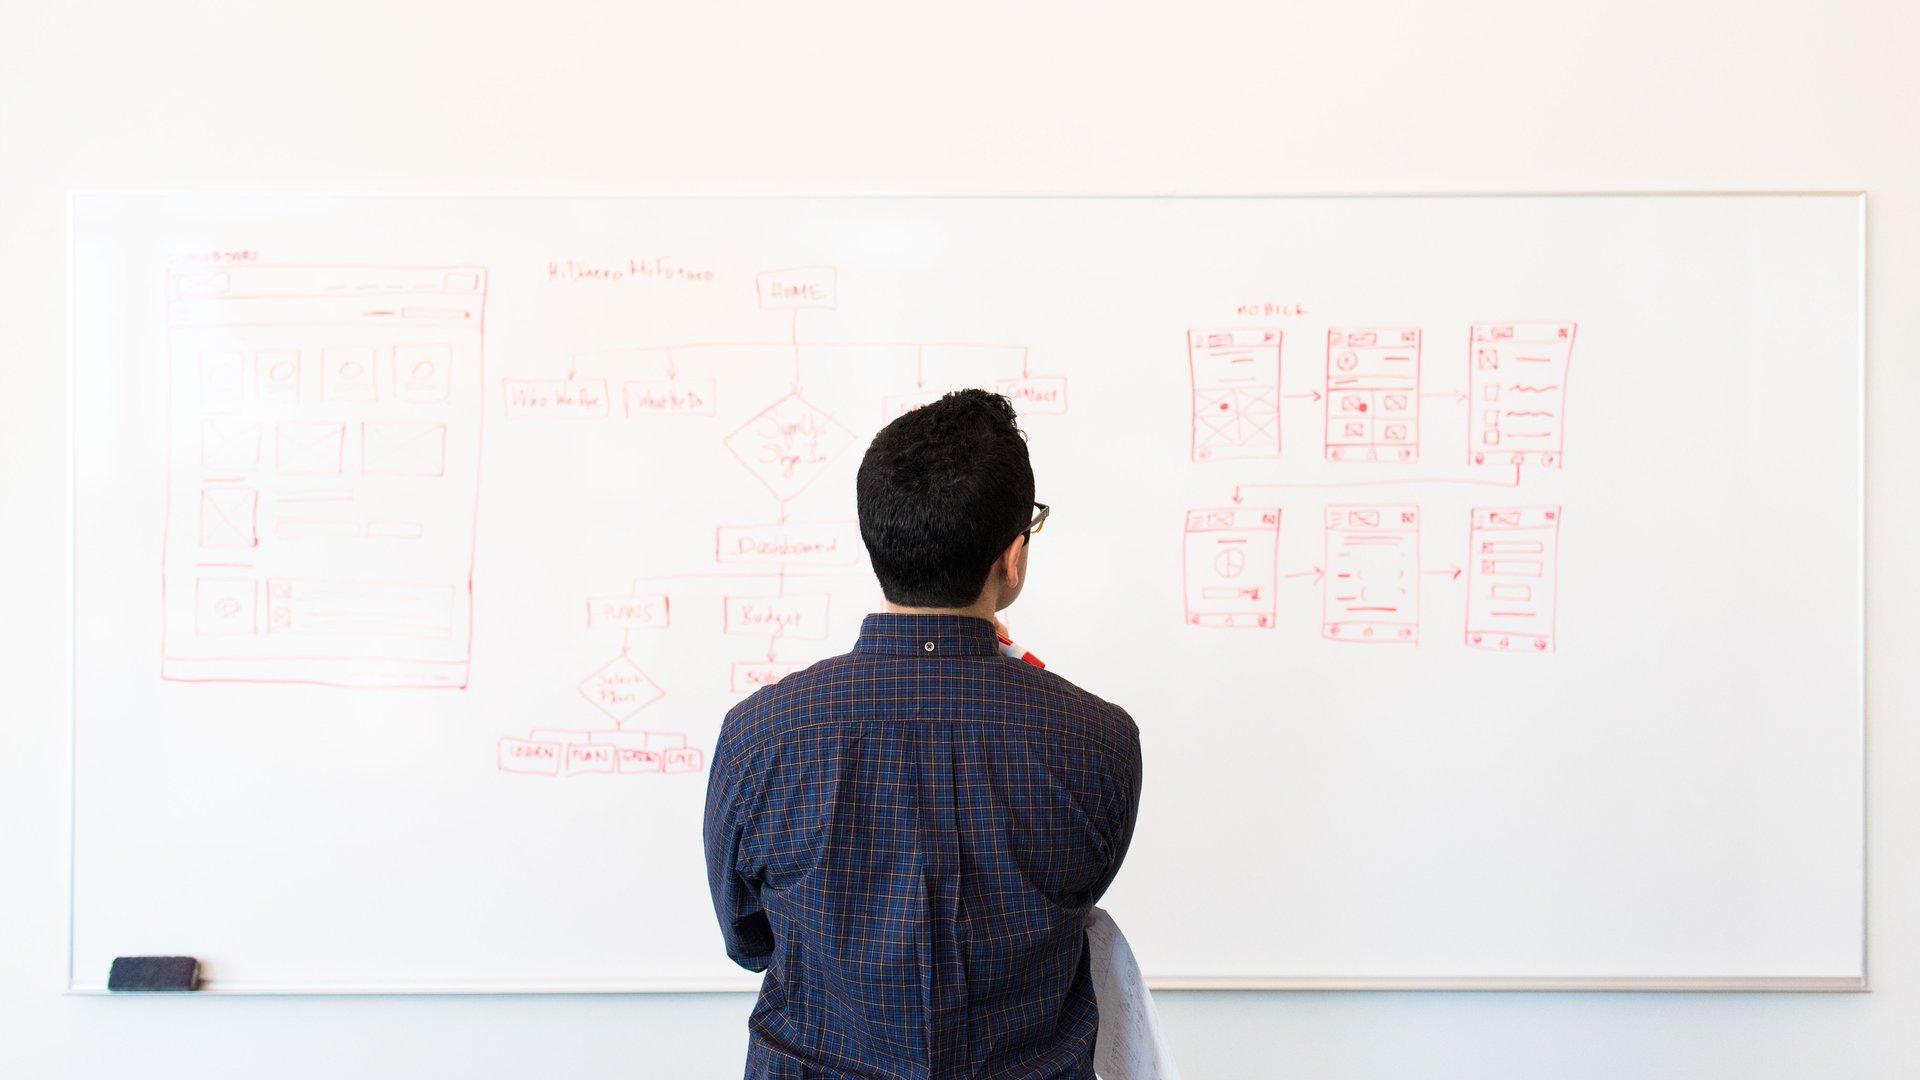
Threat modeling turns a design review into a security exercise. You map the data flows, the trust boundaries, the access control points, and the business logic, then you ask how each one fails under attack. OWASP recommends running it against your authentication, access control, and critical business flows during design refinement, and again whenever those flows change. A group booking limit, a password reset path, a checkout sequence: each one deserves the question of how an attacker abuses it. Catch the flaw on a whiteboard and you avoid the cost of catching it in production.
Secure design patterns and a paved road
Repeating secure choices beats reinventing them. A secure development lifecycle brings security specialists in from project kickoff, backed by a library of vetted components, reference architectures, and a paved-road method your developers follow by default. OWASP SAMM offers a structure for maturing these habits across teams. ISO/IEC 27001 supports the same discipline for organizations building a formal management system. The aim is plain. Make the secure path the easy path, so your developers meet the design bar without heroics.
Where training closes the gap
Insecure design is a skills problem before it is a tooling problem. Your architects and developers need to think like attackers and build resistant systems by habit. Mile2 develops the skill through role-based, hands-on certification. The Certified Secure Web Application Engineer trains developers to design and build applications which resist real attacks. The Certified Web Security Engineer covers secure web architecture and defensive design across the stack. For the attacker’s view, the Certified Professional Ethical Hacker teaches your team to find design flaws before someone else does. Pair the design work with a disciplined build process, covered in our guide to the secure software development lifecycle.
Insecure design will not surface in an automated report. It surfaces when an attacker uses your system the way you never planned. Model the threats early, build the controls into the architecture, and give your team the training to spot the gap on the whiteboard. The whiteboard is where you stop the flaw, long before it reaches your customers.