Smishing and Vishing: How Text and Voice Phishing Scams Target Canadian Organizations
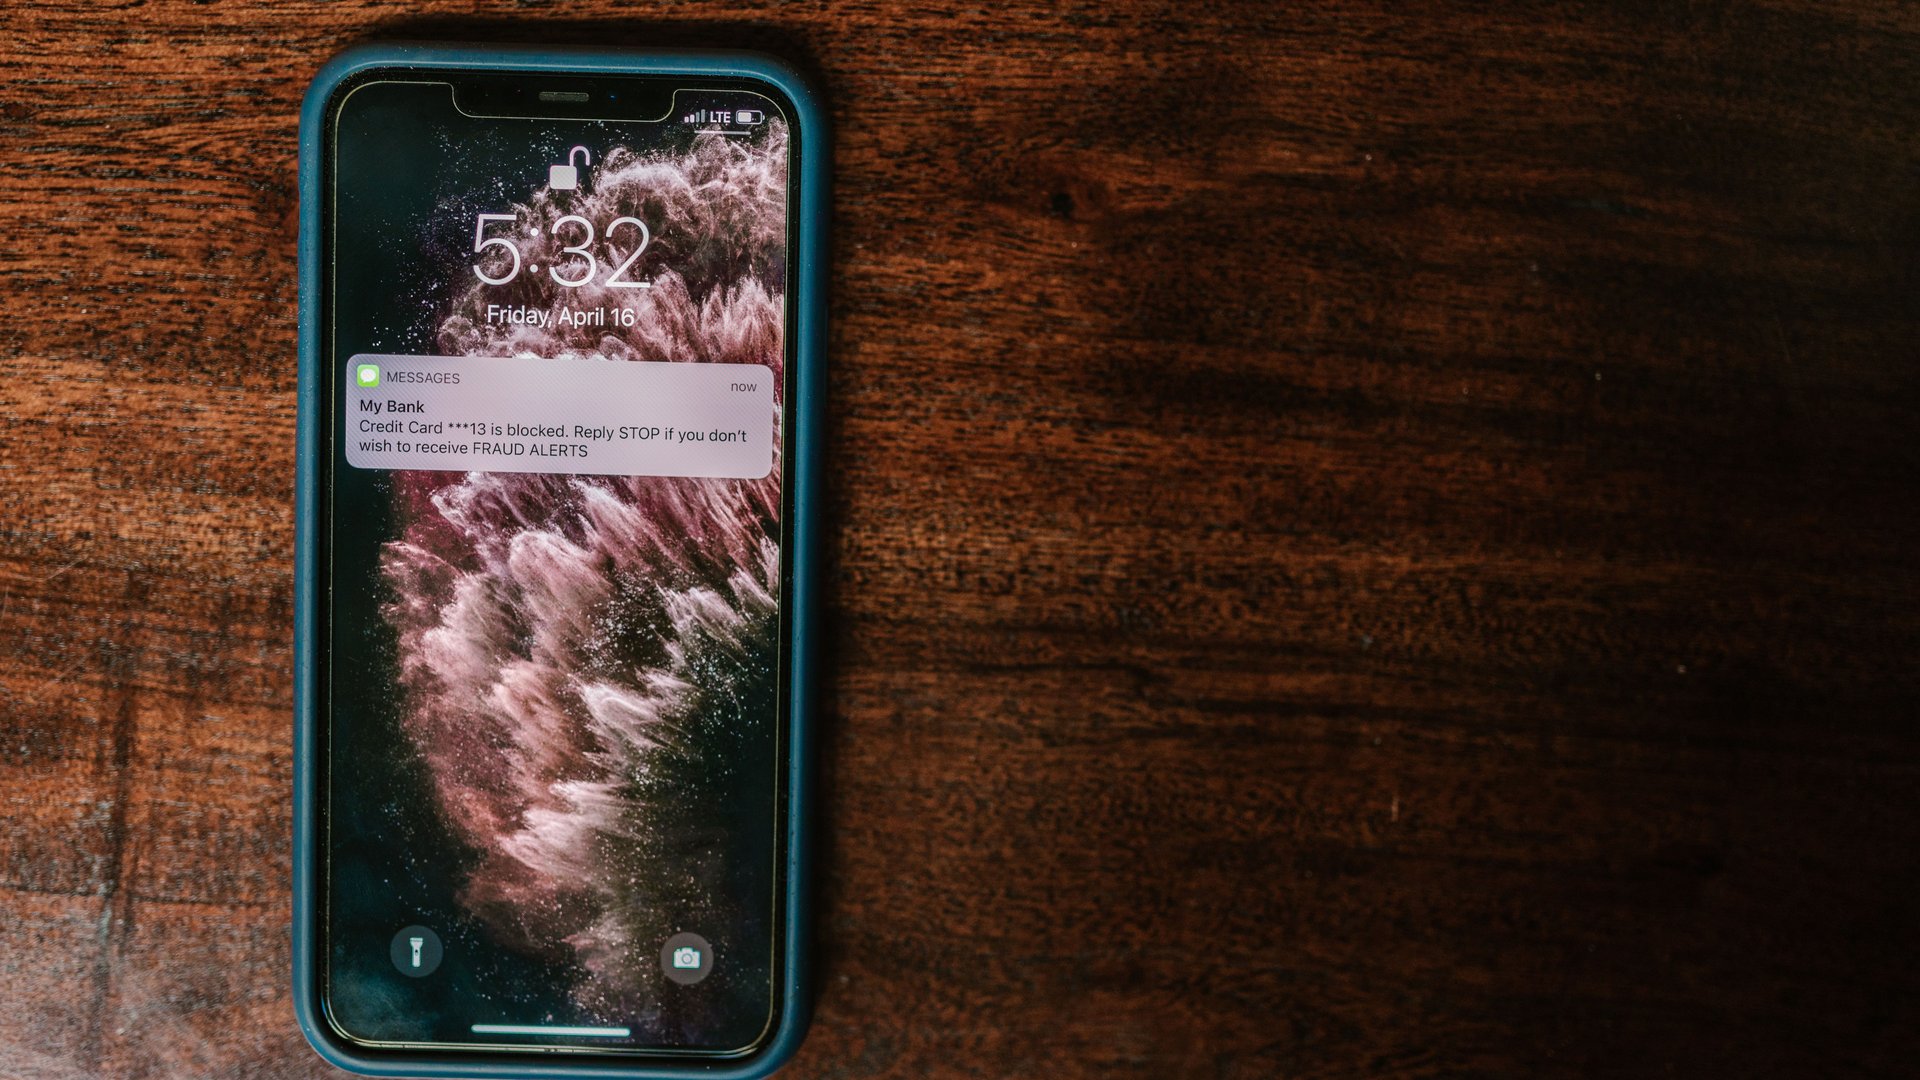
A text lands on an employee’s phone. It looks like your bank, and it sits in the same thread as real bank alerts. The message warns of a locked account and asks for a quick confirmation. Your employee taps the link. In one tap, an attacker reaches past every firewall you own, because the attack arrived on a personal phone over a channel you do not control. Text and voice phishing now cost Canadian organizations more than most leaders expect, and your business sits in the blast radius.
Smishing is phishing by text message. Vishing is phishing by phone call. Both use social engineering instead of technical exploits. The attacker skips your defences and targets the person. A convincing message, a sense of urgency, and a believable sender are enough to turn a staff member into an open door. These attacks grew fast because they work, and because your security stack rarely sees them coming.
Why Text and Voice Beat Email Filters
Your email gateway scans attachments, checks links, and quarantines known threats. A text message skips all of it. Carriers filter some spam, yet most smishing reaches the phone anyway. Phone calls face even less screening. Attackers spoof caller ID and phone numbers with ease, so a call shows a local area code or the name of a real bank. The Cyber Centre reports smishing messages even appear inside legitimate message threads, which makes them hard to spot.
What the Canadian Numbers Show
The scale is real. The Canadian Anti-Fraud Centre logged over 112,000 fraud reports in 2025 and more than 704 million dollars in reported losses. Spear phishing, the targeted cousin of these attacks, drove 67.9 million dollars of the total, the second-highest loss of any fraud type. Those figures count only reported cases. The Centre estimates most fraud goes unreported, so the true cost runs far higher. Phishing by any channel ranked among the five most reported fraud types of the year.
How Attackers Reach Your Staff
Attackers research your organization before the first message. They pull names and titles from LinkedIn and your own website. Then they pick a target and a pretext. A finance clerk gets a text from the chief executive asking for an urgent gift card purchase. A new hire gets a call from fake IT support asking for a password reset. A worker gets a text posing as a courier with a missed delivery. Each pretext borrows trust from a real relationship, and each one pushes the victim to act before thinking.
Why Your Organization Sits in the Blast Radius
A personal phone blurs the line between work and home. Your staff read work email on the same device they use for family texts. One tap on a malicious link harvests a corporate credential. One answered call hands an attacker the access code to your VPN. From there, the intruder moves into your network, reads your data, and sets up for ransomware. The weak point is not your technology. The weak point is a trusted human reached on a channel you do not manage.
How to Defend Against Smishing and Vishing
You defend against social engineering with people, process, and a few controls working together. Start with awareness. Staff need to read urgency as a warning sign, verify any unusual request through a second channel, and report suspicious texts to 7726, the national SPAM short code. Build a simple rule into your culture. No one acts on an urgent money or credential request from a text or call without confirming it by a known method first.
Layer controls behind the training. Enforce multi-factor authentication so a stolen password alone fails to grant access. Favour phishing-resistant methods like hardware keys and passkeys over text message codes, since attackers intercept one-time codes through the same channels they abuse. Give staff a fast, blameless way to report a mistake, because speed of reporting decides whether one click becomes a contained event or a full breach. These steps align with Canadian Centre for Cyber Security guidance on smishing and voice phishing, written for Canadian organizations.
Build the Skills and Culture to Stop It
Defence against smishing and vishing rests on trained people. Mile2 builds those skills at every level. The Certified Security Awareness 1 program gives your whole staff the instinct to spot a social engineering attempt and respond the right way, which turns your workforce into a sensing layer instead of a target. The Certified Incident Handling Engineer prepares your responders to contain the damage fast when someone does click. The Certified Information Systems Security Officer develops the governance judgment a security leader needs to set reporting policy, run awareness programs, and measure whether they work.
Text and voice phishing succeed because they target trust, not technology. You close the gap with steady training, clear verification rules, strong authentication, and a reporting culture with no blame. Teach your people to pause on urgency, confirm through a second channel, and report fast. Follow those steps, and the message meant to breach your organization becomes the alert warning you an attacker is knocking.