Business Email Compromise: How It Works and How to Stop It
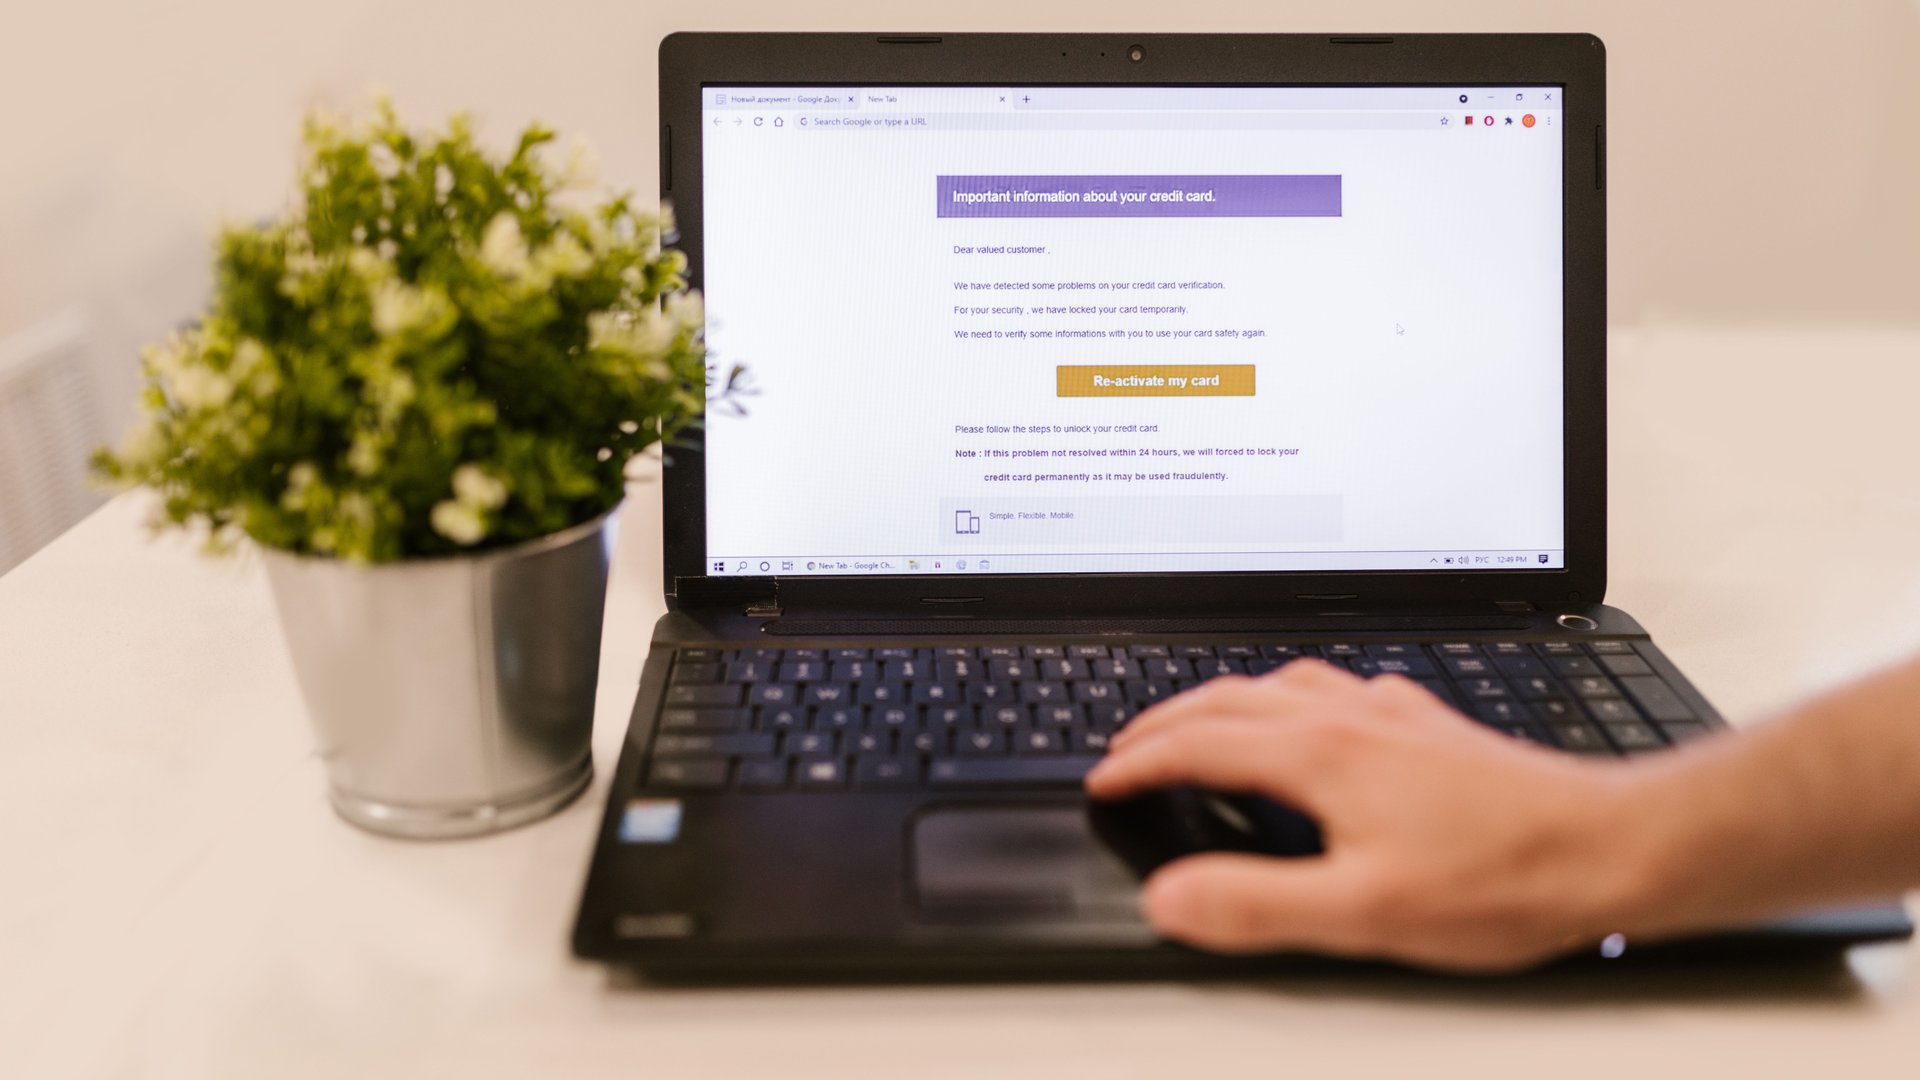
One email asks your finance clerk to move a payment to a new account. It looks like it comes from your CEO. The tone fits. The timing fits. Your clerk sends the wire. Minutes later the money sits in a criminal’s account, and getting it back grows harder by the hour. This is business email compromise, and it drains more money from Canadian organizations than almost any other fraud type.
Business email compromise, or BEC, works through trust instead of malware. A criminal studies your organization, impersonates someone your staff believe, and asks for a payment or sensitive data. No attachment. No malicious link. The request looks routine, which is why it succeeds.
How Big the Problem Is
The Canadian Anti-Fraud Centre ranks BEC among the top fraud types by dollar loss reported by Canadian businesses. Reported fraud losses across Canada reached 704 million dollars in 2025, the highest total on record. The Centre estimates only 5 to 10 percent of victims ever report, so the real national figure runs far higher. Worldwide, BEC schemes have stolen billions from organizations, and Canadian firms sit squarely in the target set.
How the Attack Unfolds
Most BEC attempts start with research. A criminal reads your public website, your team’s social profiles, and your press releases. They learn who signs off on payments, who handles vendor invoices, and when leaders travel. Then they strike during a gap, often when the impersonated executive sits out of reach and hard to verify.
Some attackers spoof a lookalike domain, swapping one letter so the address reads almost right. Others break into a real mailbox with a stolen password and send from inside your own environment. The second method proves harder to spot because the email arrives from a genuine address. Once inside, the criminal reads live conversations, waits for a real invoice, and changes the payment details at the last moment.
Why Traditional Defences Miss It
Spam filters look for malware and known bad links. BEC carries neither. The message reads like normal business. Your firewall sees nothing wrong. Your antivirus stays quiet. The attack targets human judgment under pressure, not your network perimeter. This gap explains why technical controls alone leave you exposed.
Attackers add urgency on purpose. They write “handle this before the deal closes” or “I need this done in the next hour.” Pressure shrinks the time your staff spend checking. The Canadian Centre for Cyber Security describes this pattern in its social engineering guidance, where a trusted identity paired with urgency drives a rushed decision.
The Controls to Stop BEC
Start with payment verification. Require a second channel for any change to banking details and for any wire above a set threshold. A quick phone call to a known number stops most fraudulent transfers. Write the rule into policy so no single person moves large sums alone.
Strengthen your email accounts next. Phishing-resistant multi-factor authentication blocks the account-takeover route criminals favour. Even when a password leaks, the attacker fails the second check. Pair this with monitoring for unusual mailbox rules, since attackers often create hidden forwarding rules to watch a compromised inbox.
Train your people with real scenarios. Generic awareness slides do little. Staff need to see a sample executive-impersonation email, spot the lookalike domain, and practise the verification step. Finance and procurement teams deserve extra attention because they hold the payment authority attackers want. The RCMP lists these same habits as the frontline defence against the scam.
Building the Skills In-House
Stopping BEC needs more than one tool. You need people who understand social engineering, incident response, and risk. Structured, role-based training builds those skills across your team.
Awareness training gives every employee the habit of questioning a suspicious request. The Certified Security Awareness 1 course sets this baseline. For the people who respond when an attack lands, the Certified Incident Handling Engineer path teaches how to contain a compromise and recover funds fast.
Leaders and security officers need the wider view. The Certified Information Systems Security Officer program covers the governance and controls behind payment verification and access management. When your focus sits on measuring and reducing exposure, the Certified Information Security Risk Manager path ties BEC defence to a formal risk framework.
What to Do This Week
Review your payment approval rules. Confirm every banking change needs a second channel. Turn on phishing-resistant MFA for all email accounts, starting with finance and executives. Check your mailboxes for unexpected forwarding rules. Then brief your team with one real BEC example.
Report every attempt, successful or not, to the Canadian Anti-Fraud Centre and to the Canadian Centre for Cyber Security. Fast reporting improves the odds of recovering a wire and helps warn other organizations. BEC succeeds on speed and silence. Your defence works on verification and voice. Build both into how your organization handles money, and you remove the opening these criminals rely on.