Cyber Liability Insurance in Canada: What IT Leaders Need to Know
Your cyber insurance renewal now reads like a security audit. Insurers want proof of multi-factor authentication, tested backups, and endpoint protection before they quote a price, and one missing control raises your premium or voids a claim. For Canadian IT leaders, the policy has become a test of how well you run security, not a safety net you buy and forget.
Cyber liability insurance covers the cost of recovering from an attack. Think ransomware payments, forensic investigation, legal fees, breach notification, and lost revenue during downtime. The coverage matters because attacks hit Canadian organizations every day. Statistics Canada found 16 percent of businesses faced a cyber security incident in 2023, and recovery costs climb fast once systems go down.
Adoption is rising, but slowly
Coverage is growing across Canada. Statistics Canada reported 22 percent of businesses held cyber risk insurance in 2023, up from 16 percent in 2021. Among firms with a policy, 53 percent had coverage for direct losses, 44 percent for restoring software and data, and 39 percent for business interruption. You read those numbers two ways. Uptake climbs each year, and most Canadian organizations still carry no coverage at all.
The gap widens for smaller firms. The Insurance Bureau of Canada surveyed business owners in August 2025 and found only 12 percent held a stand-alone cyber policy. Fewer than half believed their business faced any real risk, even as the Business Development Bank of Canada reported 73 percent of small businesses had already lived through an incident.
What insurers demand before they quote
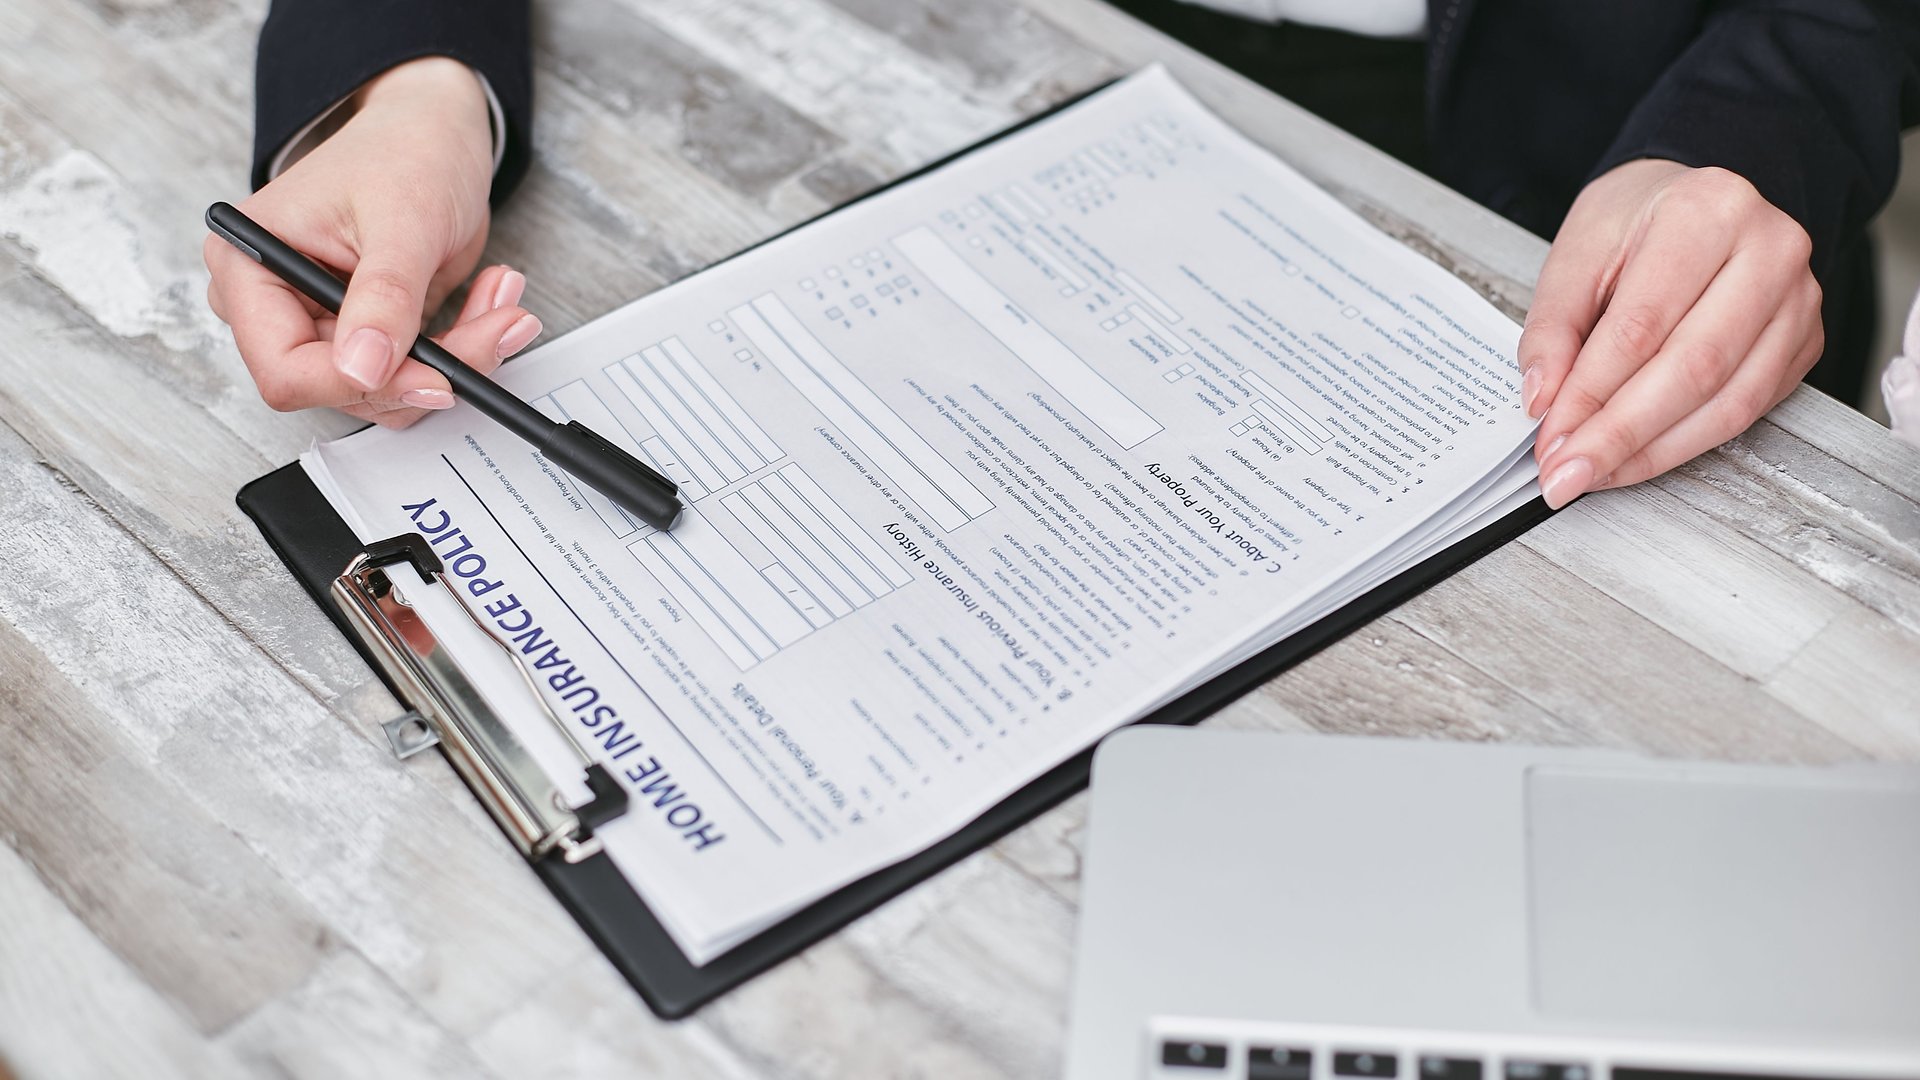
Underwriting has tightened. Insurers no longer accept a signed form and a handshake. They want evidence. Expect to show multi-factor authentication on every account, endpoint detection and response on all devices, offline or immutable backups you test on a schedule, and patch management with a clear deadline for critical fixes. A modern application runs 8 to 25 pages and asks for configuration screenshots, vendor invoices, and signed attestations.
The 2024 CIRA Cybersecurity Survey showed how insurers changed terms with existing clients. 39 percent verified current security measures, 38 percent raised premiums, and 37 percent altered the rules for getting or renewing a policy. When your controls slip, your price rises or your coverage disappears.
Claim denials follow the same logic. When you attest to a control you do not run, and an incident traces back to the gap, the insurer has grounds to refuse payment. The policy you thought protected you turns into a paper promise. Accurate answers on the application protect you more than optimistic ones do.
Map your controls to a Canadian baseline
You do not need to guess what good security looks like. The Canadian Centre for Cyber Security publishes Baseline Cyber Security Controls for Small and Medium Organizations, and its list overlaps almost point for point with insurer requirements. Multi-factor authentication, backups, patching, and access control all appear. For larger and government-facing organizations, ITSG-33 sets the control framework the federal government uses. Align to these first, then treat NIST CSF and ISO 27001 as the international reference points they mirror.
PIPEDA adds another reason to prepare. The federal privacy law requires you to report breaches involving a real risk of significant harm. Insurers know this, and they price the cost of notification and legal response into your policy. Strong documentation lowers both your regulatory exposure and your premium.
Training is the control most buyers ignore
Technical controls get the attention, but people cause most breaches. Phishing and stolen credentials open the door for ransomware. Insurers have noticed, and many now ask whether you run security awareness training and how often. A workforce trained to spot a suspicious email lowers your claim frequency, and a lower claim history earns a better renewal.
This is where training pays for itself twice. Structured programs like the Certified Security Awareness 1 course give staff the habits insurers reward. For the people who own risk decisions, the Certified Information Security Risk Manager path teaches how to assess exposure, document controls, and speak the language underwriters use.
Who should own the policy
Cyber insurance sits between IT, finance, and legal, and it needs one owner who understands all three. In most Canadian organizations, a security manager or risk lead fills the seat. They read the policy exclusions, confirm the stated controls match reality, and keep evidence ready for renewal. The Certified Information Systems Security Manager and Certified Information Systems Security Officer programs build this skill set, tying governance to the day-to-day operations an insurer inspects.
Treat the policy as a working document, not a filing-cabinet purchase. Review it each year against your current controls. Close the gaps insurers flag before they cost you a claim. A cyber liability policy protects your organization only when the security behind it holds up, and building this security is work your team owns every day.