What Is Identity and Access Management (IAM) and Why Does It Matter?
A former employee still logs in three weeks after their last day. A junior technician holds admin rights nobody remembers granting. A shared service account uses a password five people know. None of these needs an attacker to become a breach. Each one is a gap in identity and access management, and each one hands an intruder a working key to your systems.
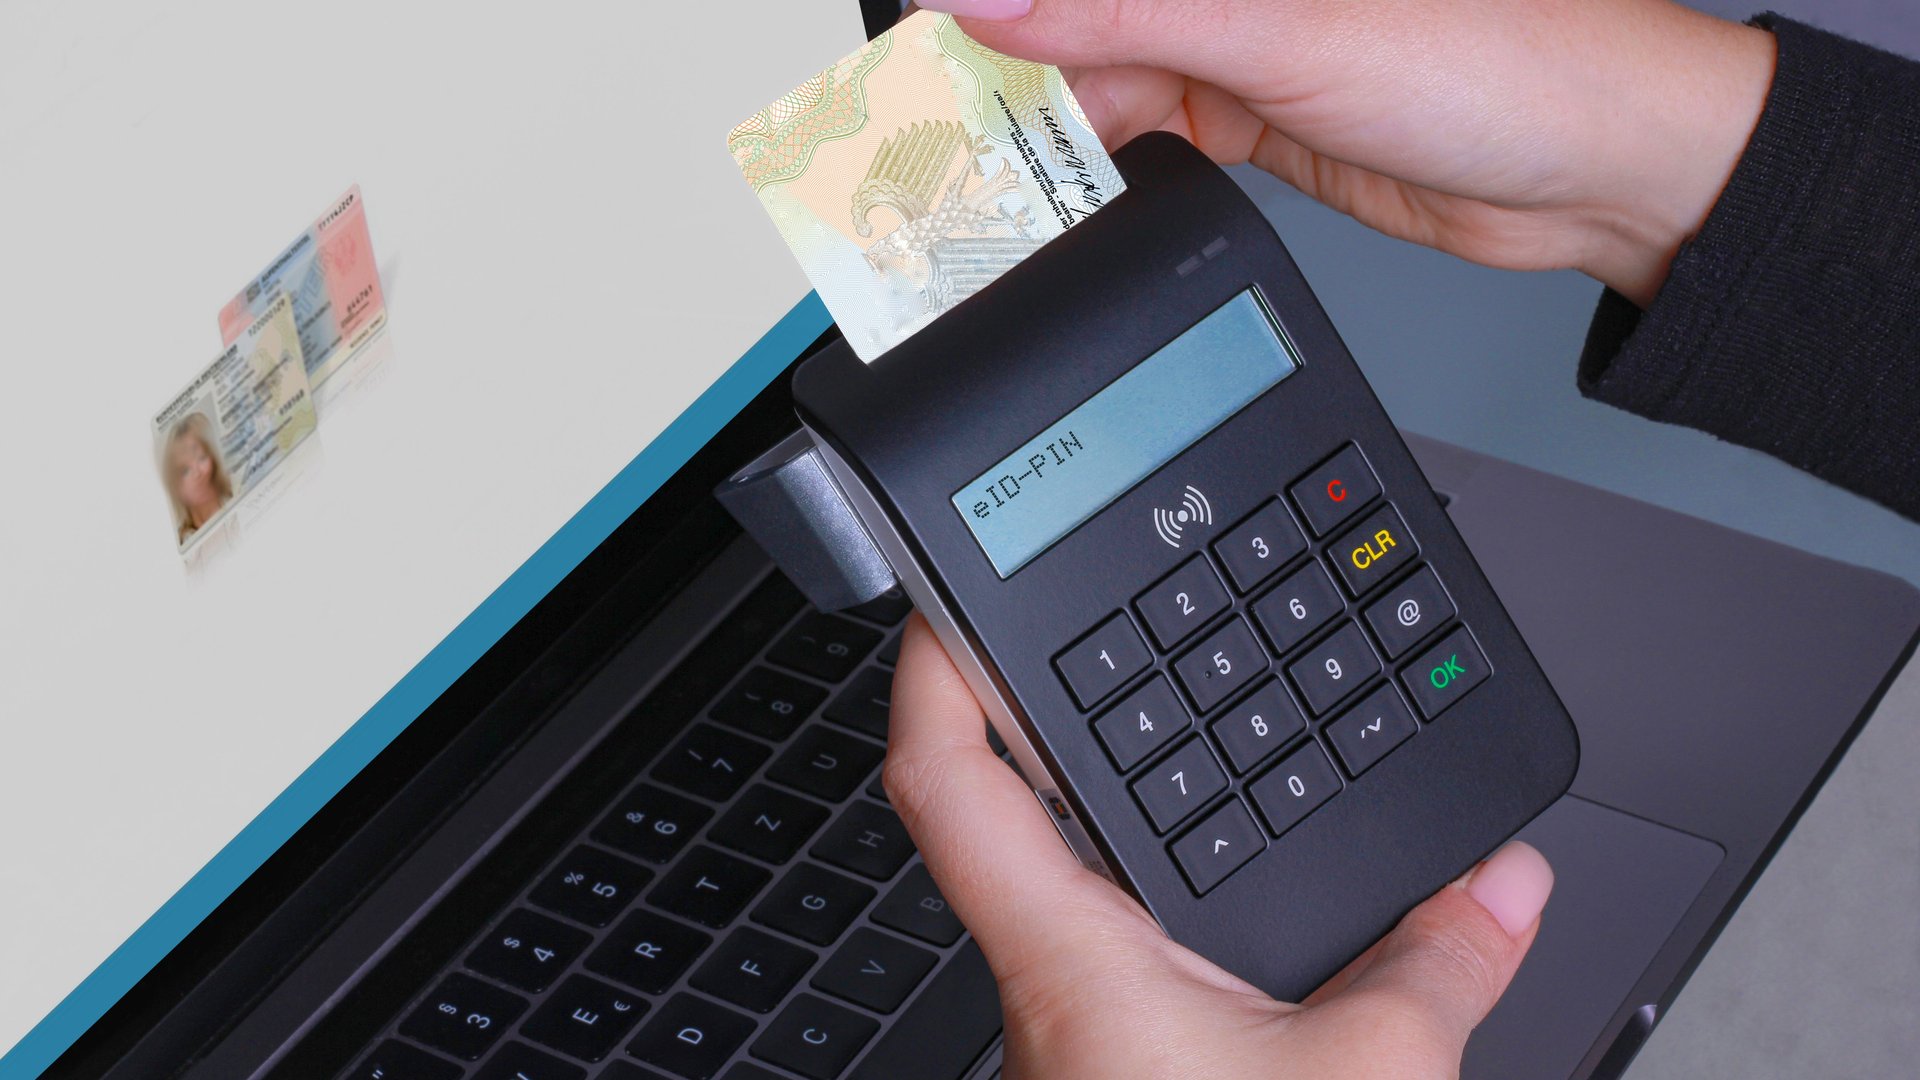
Identity and access management, or IAM, controls who reaches your systems and what they do once inside. It answers two questions every login raises. Who are you? And what are you allowed to reach? IAM ties a verified identity to a defined set of permissions. Get it right and the wrong people stay out while the right people work without friction. Get it wrong and one stolen credential opens the whole network.
Why Identity Became the New Perimeter
Firewalls once marked the edge of your network. Remote work, cloud services, and mobile devices erased the old edge. Your people now sign in from home routers, coffee shops, and personal laptops. Identity is the one control point left. Attackers know this. Compromised credentials remain among the most common routes into an organization, and breaches driven by stolen credentials cost Canadian and global firms millions per incident. When identity is the perimeter, weak access control is an open door.
The Cost of Getting Access Wrong
The numbers make the case. The average Canadian data breach hit CA$7.11 million in 2026, the highest total IBM has recorded since it began tracking the figure. Breaches traced to compromised credentials ran about 4.67 million US dollars each. Customer personal information was exposed in more than half of all breaches. Behind most of these figures sits an access failure. An account with too many rights. A login nobody disabled. A password reused across services. IAM exists to close these gaps before they cost you.
The Building Blocks of IAM
The Canadian Centre for Cyber Security frames IAM around three linked functions in its guidance on identity, credential, and access management. First comes identification, where a user claims an identity with something like a username. Next comes authentication, where the system confirms the claim through a password, a token, a fingerprint, or a mix of these. Last comes authorization, where the system grants access to the resources the role allows and blocks the rest. Each function depends on the one before it. Weak authentication undermines even the tightest authorization rules.
Multi-Factor Authentication and Least Privilege
Two principles do most of the heavy lifting. Multi-factor authentication asks for more than a password, so a stolen credential alone fails to get in. The Cyber Centre sets multi-factor authentication as a baseline expectation in its user authentication guidance and recommends it for organizations of every size. Least privilege gives each person the minimum access their job needs and nothing more. When an account holds only the rights it uses, a compromised login does far less damage. Pair the two and you shrink both the odds of a breach and its blast radius.
IAM and the Move to Zero Trust
IAM forms the foundation of a zero trust model. Zero trust drops the assumption anything inside the network is safe. It checks every request, every time, against identity and context. Without strong IAM, zero trust has nothing to verify against. Role-based access control, regular access reviews, and prompt removal of accounts when people leave turn zero trust from a slogan into a working practice. Canadian frameworks like ITSG-33 build access control and identification requirements into their control catalogue, giving public sector teams a clear standard to measure against.
The Skills Behind a Working IAM Program
Tools alone do not secure identity. Someone has to design the access model, review who holds which rights, and investigate odd login behaviour. A security analyst monitors access events and spots the anomalies a rule misses. The Certified Cybersecurity Analyst program builds the monitoring and investigation skills an IAM operator relies on. Above the analyst sits governance. Someone decides the access policy, maps it to PIPEDA and internal rules, and owns the outcome. The Certified Information Systems Security Officer track prepares managers to lead this decision layer.
For teams building a formal risk program, IAM is one control among many. The Certified Information Security Risk Manager certification frames access control as a treatment for the risk of unauthorized entry, and helps leaders weigh it against other priorities. Cloud environments add their own identity challenges, from federated logins to machine identities. The Certified Cloud Security Officer program covers how IAM works across cloud platforms where traditional perimeter thinking breaks down.
Where to Start
Begin with an inventory. List every account, every privileged login, and every service credential across your systems. Disable what nobody uses. Cut rights nobody needs. Turn on multi-factor authentication everywhere it fits, starting with admin and remote access. Set a schedule to review access, and tie account removal to your offboarding process so no login outlives the person who owned it. Identity and access management is not a one-time project. It is a discipline you run every day. The organizations breached through a forgotten account are rarely the ones reviewing access. They are the ones who assumed the door was already locked.