Secure Software Development Lifecycle: How to Build Security Into Your Code
A practical guide to the secure software development lifecycle for Canadian teams, with security built into every phase from design to deployment.
A practical guide to the secure software development lifecycle for Canadian teams, with security built into every phase from design to deployment.
Unpatched software caused one in three breaches last year. Build a patch management program on the CCCS risk schedule and close the gap.
Most breaches start with a stolen admin login, not a broken lock. Privileged access management takes those keys off the table. Here is how to begin.
Email spoofing lets criminals send mail from your domain. DMARC, built on SPF and DKIM, shuts it down, and reject is the policy to reach.
SOAR connects your security tools and automates the first response to threats. See how Canadian SOC teams use it to act faster with fewer people.
A DDoS attack floods your servers until real users cannot get through. See how the attack works and how Canadian organizations defend against it.
Weak default passwords and missing updates turn connected devices into open doors. Learn how to secure IoT across your Canadian organization.
Quantum computers will break today’s encryption. Canada set deadlines through 2035. Learn what post-quantum cryptography is and how to prepare now.
APIs now carry more traffic than users and draw more attacks. Learn why APIs are the top attack surface and how to secure them under Canadian guidance.
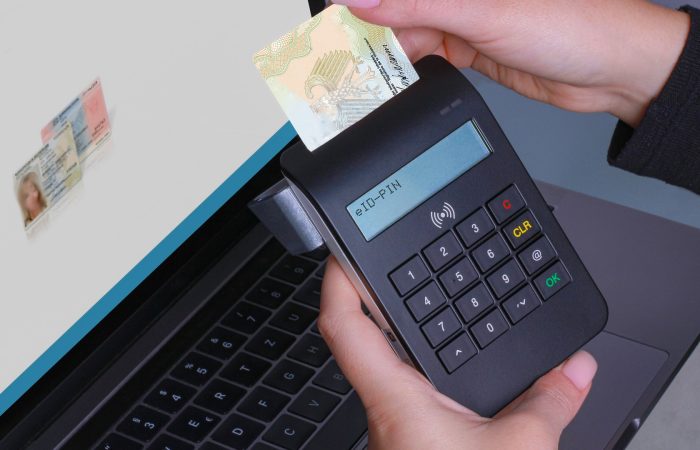
Identity and access management decides who reaches your systems and what they do there. Learn how IAM works and why it anchors Canadian security.